
3 min read
Security
Introducing VDP (Vulnerability Disclosure Program) Kaizen Activities

This summary was generated by AI. Please refer to the article for accurate details.
Read the summary
We launched a new Vulnerability Disclosure Program (VDP) to make it easier for security researchers to report issues. Before this, most reports were unclear or didn’t actually involve real vulnerabilities in our systems. Now, with a clear process, we’ve received six reports—two of which were confirmed and fixed. That’s a 33% success rate in actionable issues, which surprised us and shows real progress. To improve the process, we adopted IssueHunt’s VDP service in November 2024. We updated our guidelines to clearly state that we don’t offer bounties, defined which services are covered, and created a standard report template. This helped researchers submit better, more accurate reports. As a result, the quality of incoming reports improved significantly. By March 7, 2025, we had six reports in total. Two were confirmed vulnerabilities that required action and have been fixed. The response time from report to fix was under 72 hours for both cases. That’s fast, especially for a company without a reward program, showing our team is responsive and effective. We also joined IssueHunt’s P3NFEST Bug Bounty 2025 Winter, offering students a chance to find bugs on our corporate site and tech blog. The event runs from February 17 to March 31, 2025. Though we don’t offer rewards, this helps students gain hands-on experience and strengthens the broader security ecosystem. It’s a small step toward building a more secure internet.
Self-Introduction
My name is Morino, and I work at KINTO Technologies, mainly in product security and security governance. I'm a fan of RB Omiya Ardija and Chiikawa. For the past 10 years, I've been involved in cybersecurity and information security. Prior to that, I spent many years as a web application engineer, focusing on the development and operation of web performance measurement systems and front-end platforms for e-commerce sites. In this article, I’d like to share our Kaizen efforts related to the Vulnerability Disclosure Program (VDP).
What is the Vulnerability Disclosure Program (VDP)?
The VDP is a system that enables companies and organizations to receive vulnerability reports from external security researchers and white hat hackers. Public awareness grew in October 2023 when Rakuten Group placed a "security.txt" on a public server and launched its VDP.
Reference: Rakuten places text on public server — "security.txt" to help improve security (in Japanese)
What is security.txt?
Published as RFC 9116 in April 2022, security.txt: A File Format to Aid in Security Vulnerability Disclosure helps standardize how companies and organizations share vulnerability reporting information, making it easier for security researchers to report issues. We also published our own security.txt in November 2023.

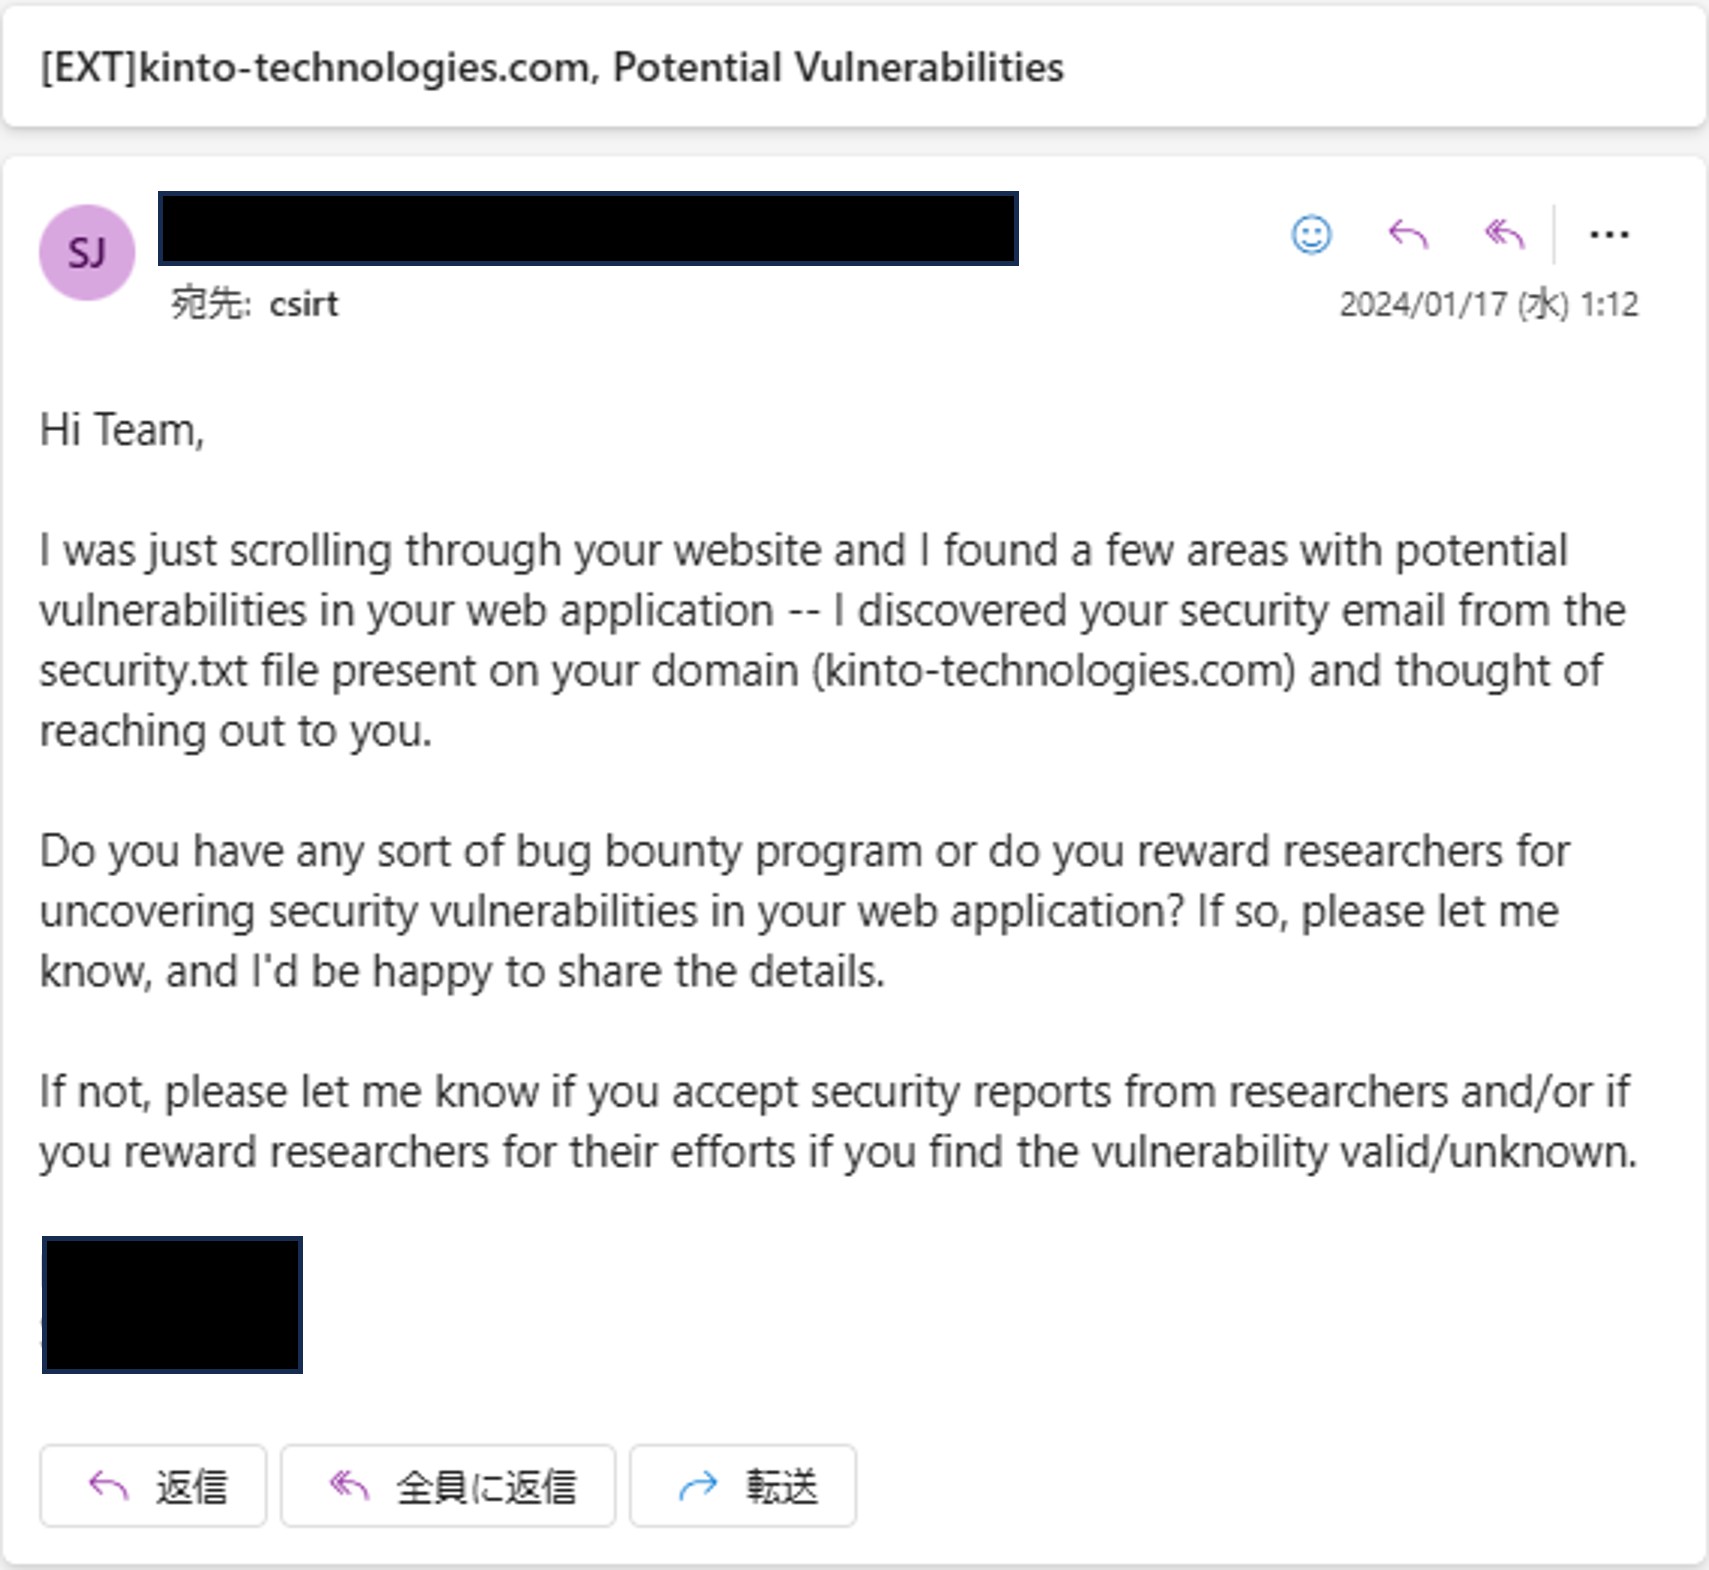
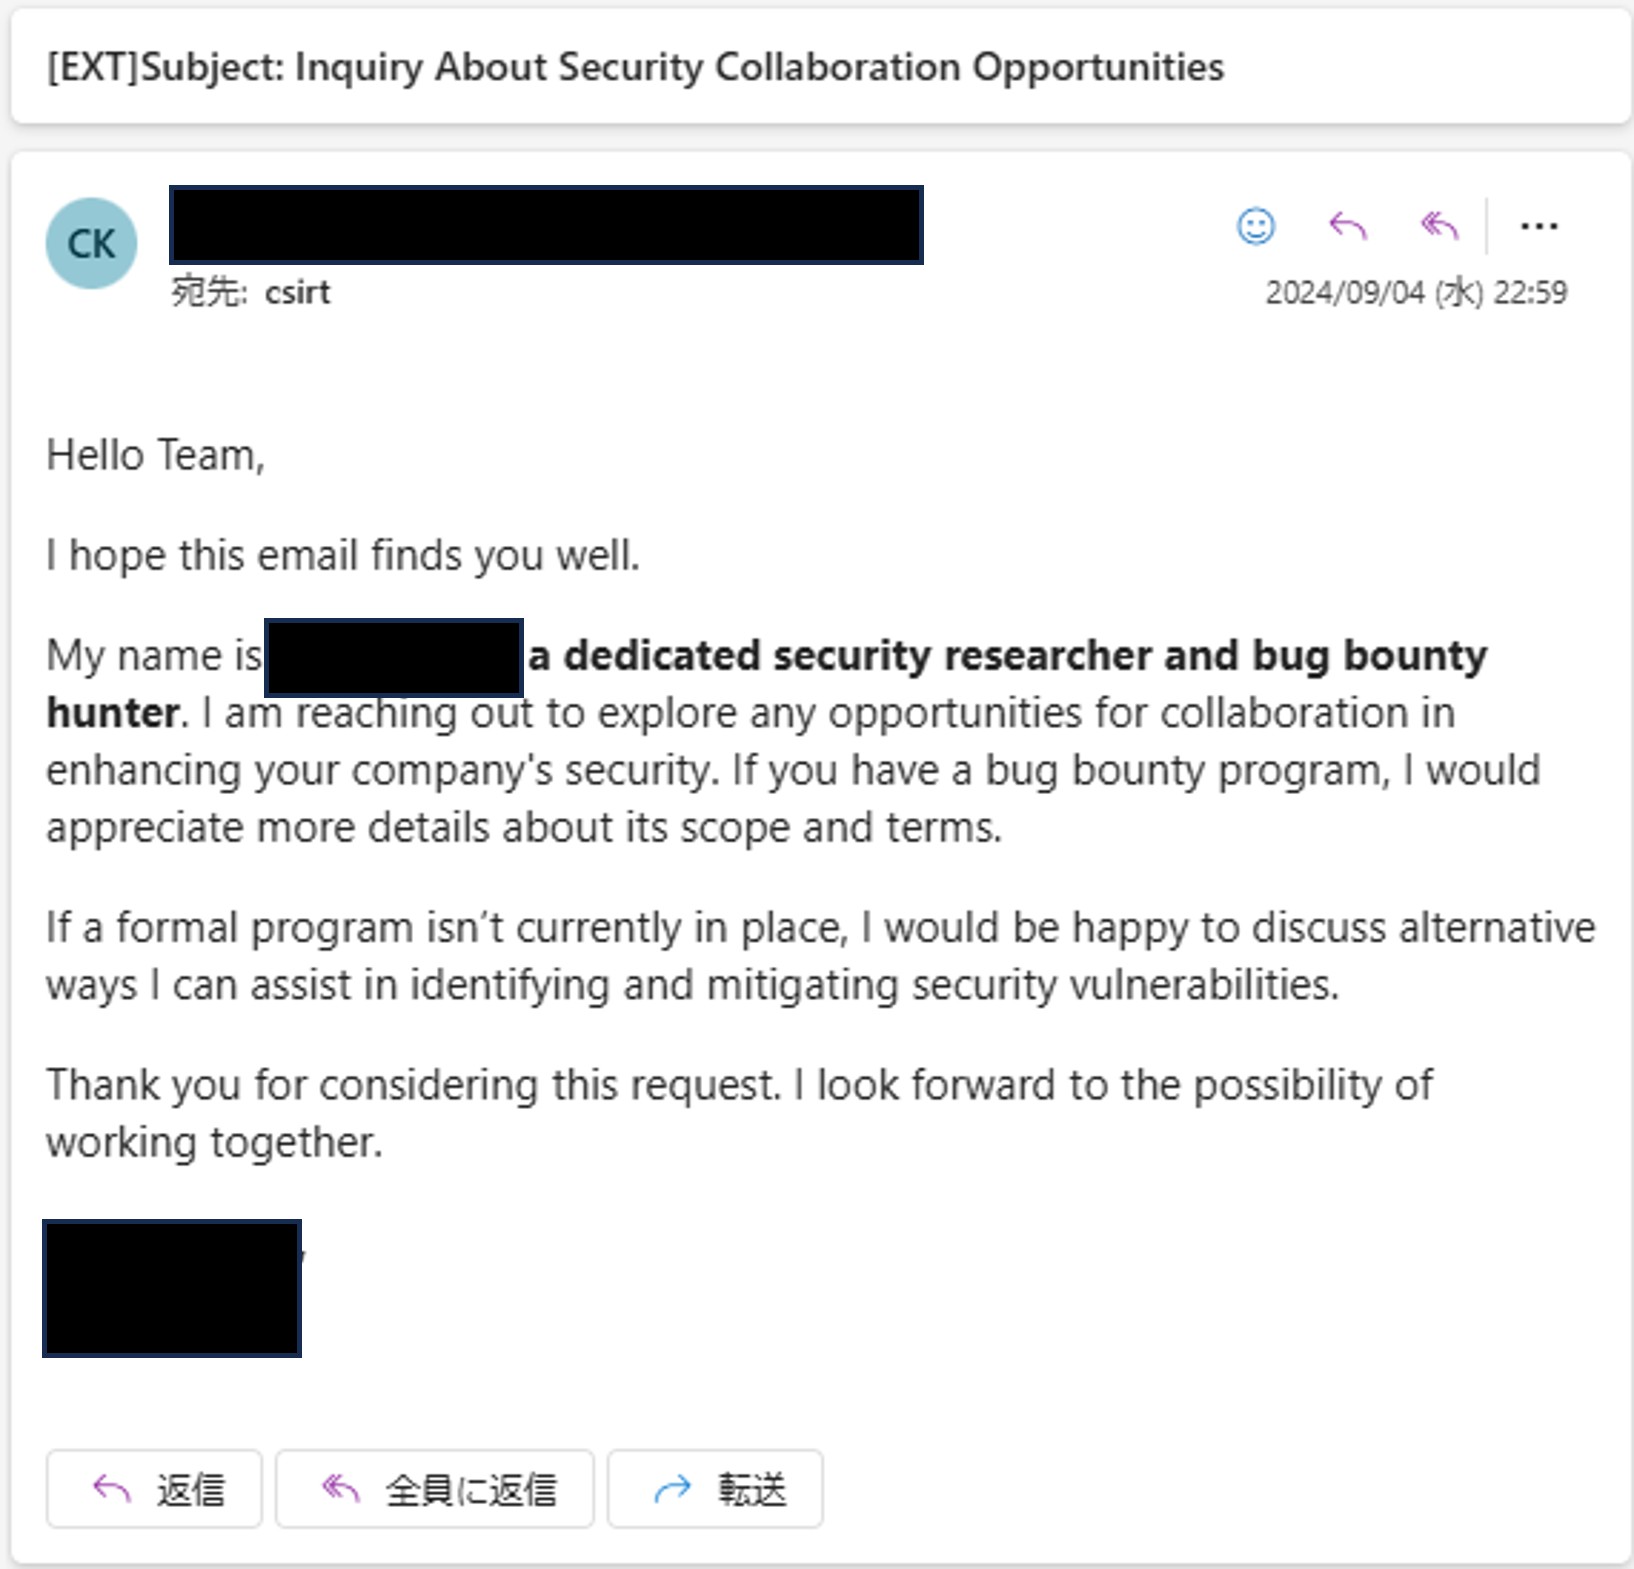
Reactions After Installing security.txt
Most inquiries were about whether we offer rewards (we don't), and many reports didn't clearly indicate whether they actually involved vulnerabilities in KINTO/KTC.
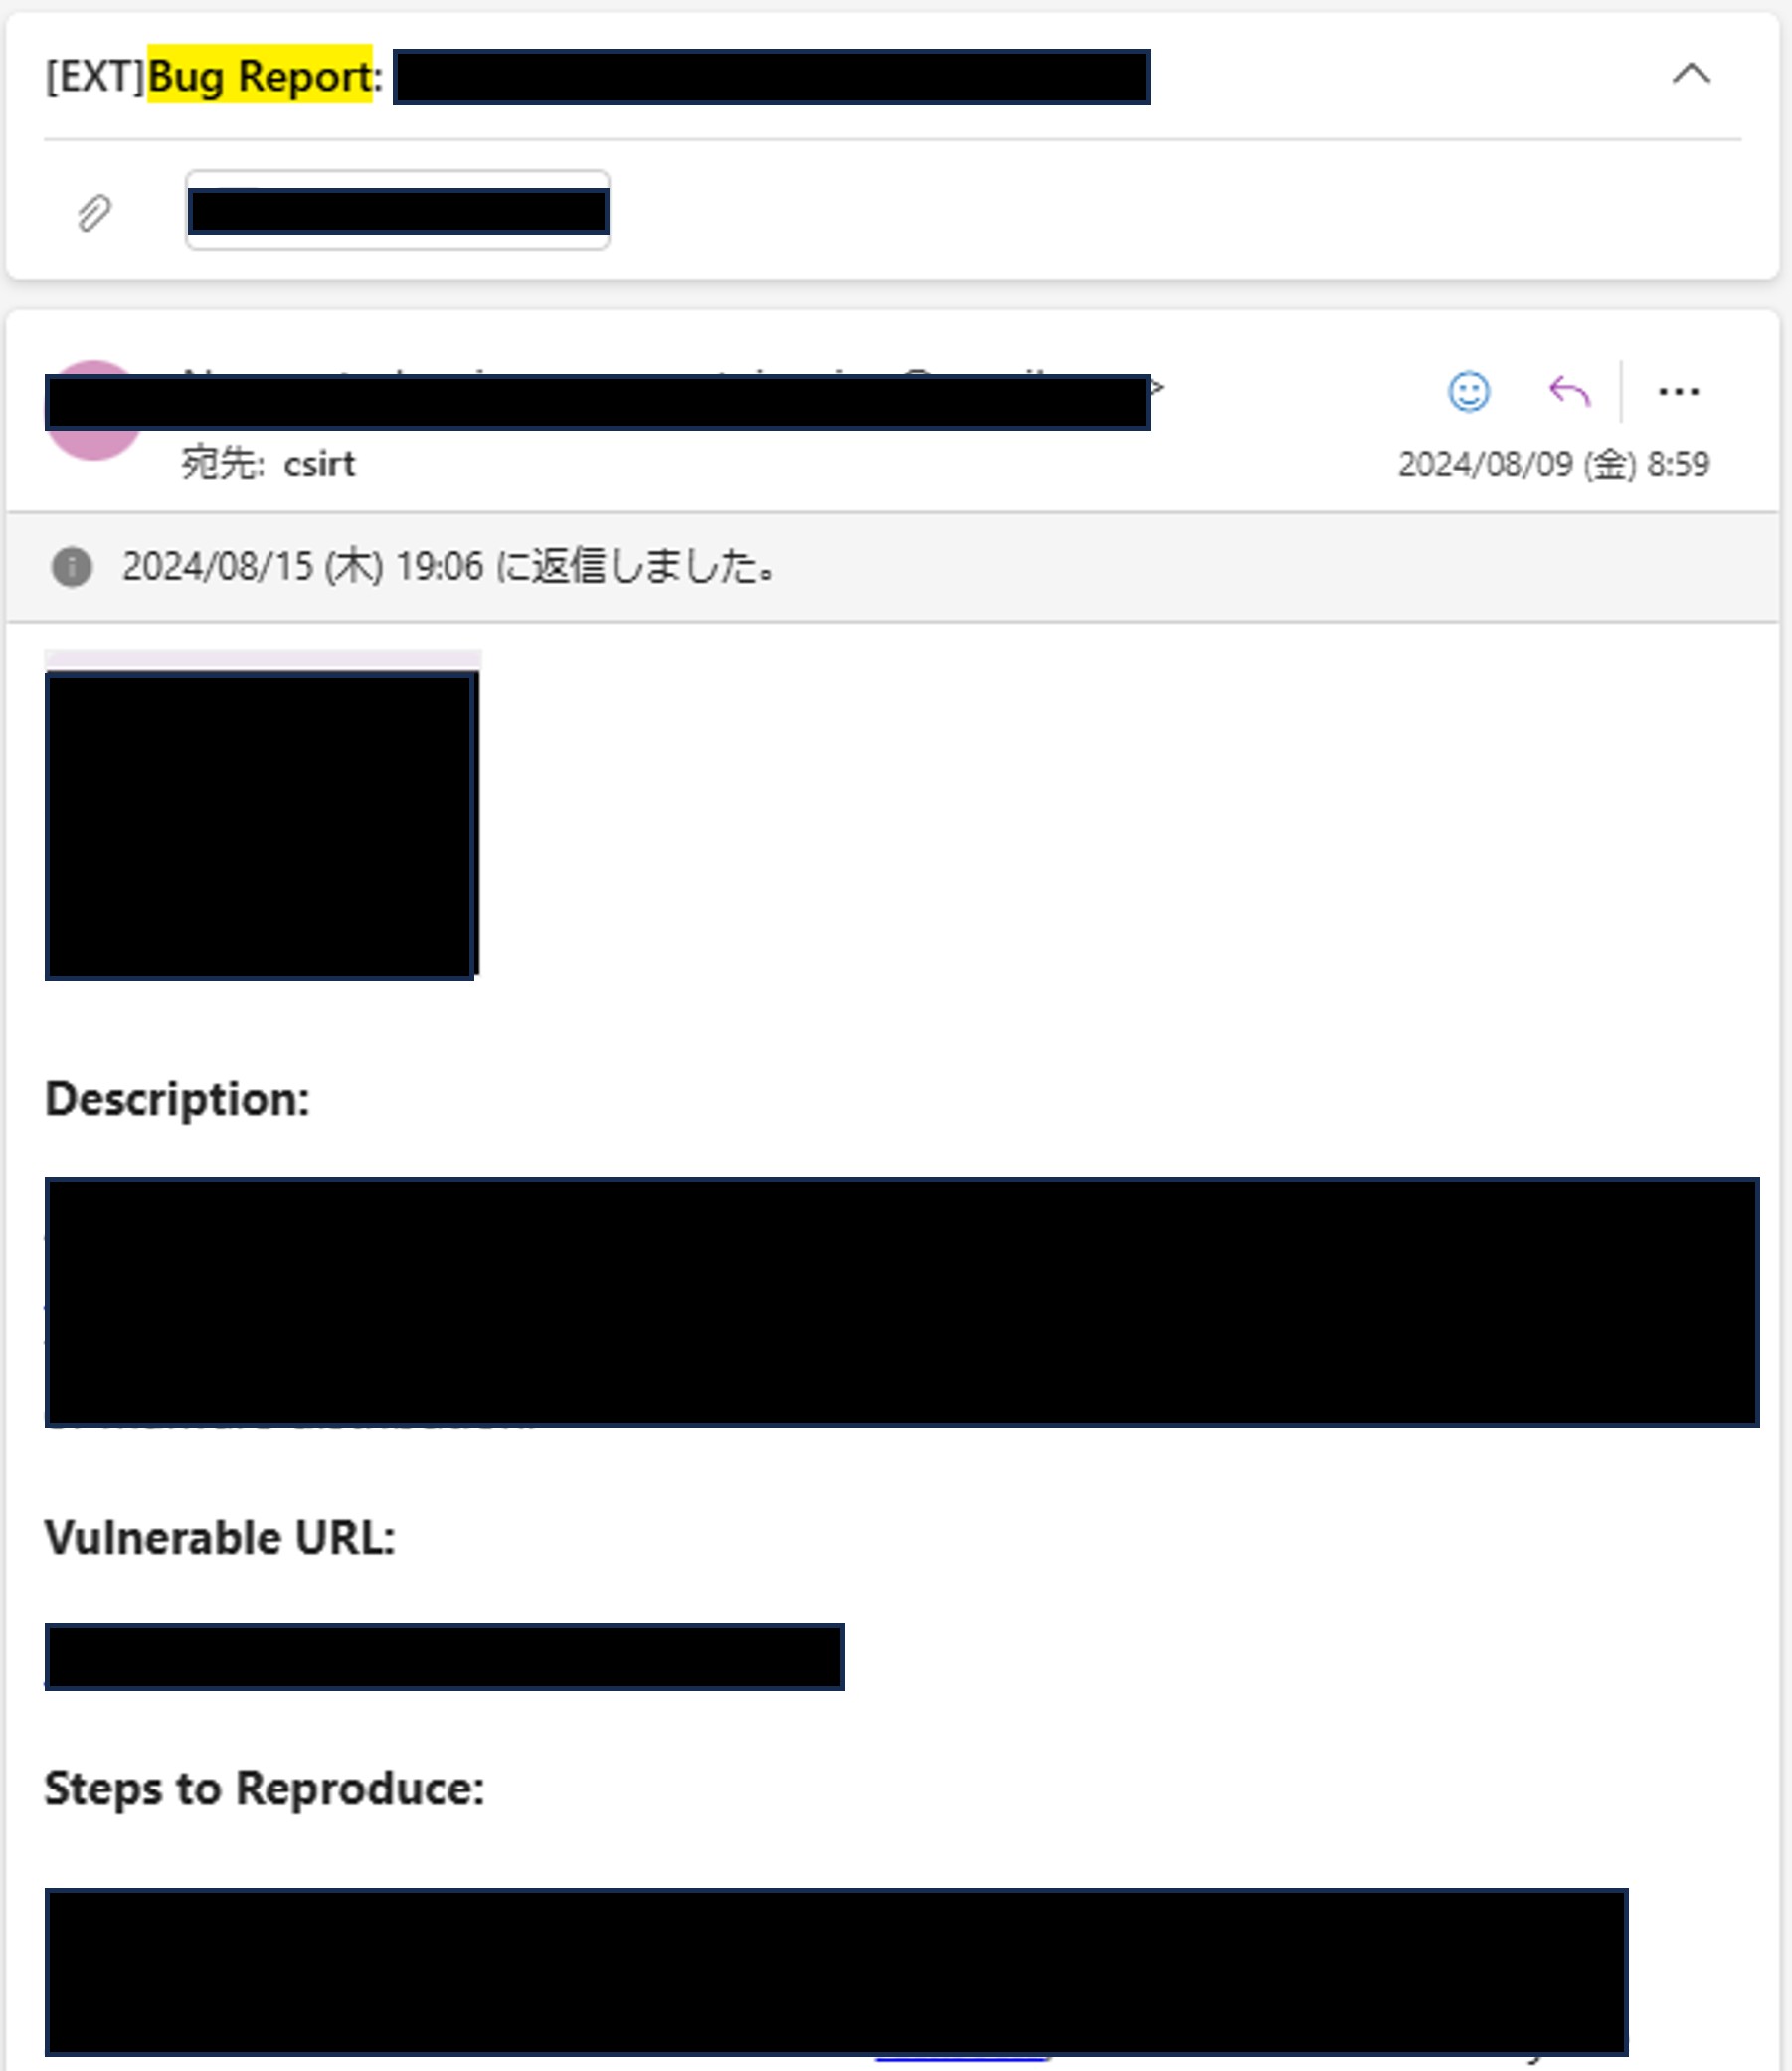
A White Hat Hacker Reported a Vulnerability!
In August 2024, we received a report about a vulnerability in our service. After reviewing the report within our team, we confirmed the issue was real and asked the development team to fix it.
Kaizen for Our VDP
Although we recognized the value of the VDP, we identified several issues. As a result, we started using the VDP service offered by IssueHunt in November 2024.
- Clarify VDP guidelines, including whether a bounty is offered
- Specify which web services and applications are covered
- Provide a report template
As of March 7, 2025, we've received six reports; two of which involved vulnerabilities that required action and have been fixed. Honestly, I'm surprised at the results, which exceeded my expectations.
Our company is featured as a case study on the IssueHunt website. Please have a look if you're interested.
A fresh perspective on boosting security! VDP success story in the car subscription industry (in Japanese)
Our Contribution to the P3NFEST Bug Bounty 2025 Winter
As mentioned above, we do not currently offer a rewards program. However, to evaluate the effectiveness of incentive-based systems and to support students working to secure the future of the internet we’ve decided to contribute some of our services to a student-focused bug bounty program hosted by IssueHunt.
The following services are eligible for bug bounties:
- KINTO Technologies Corporate Site
- KINTO Tech Blog (this website)
The event runs from Monday, February 17, 2025 to Monday, March 31, 2025.
For more information, please visit the event page. We welcome students to take on the challenge. P3NFEST Bug Bounty 2025 Winter
関連記事 | Related Posts


We are hiring!
【PdM】オープンポジション/東京・名古屋・大阪
募集背景KINTOテクノロジーズでは新たな事業展開と共に開発するプロダクトが拡大しています。サービスの新規立ち上げ、立ち上げたプロダクトのグロースを推進し、KINTOの事業展開を支えるプロダクトマネージャーを求めています。
【Java/Python】事業や組織の成長に携わるプロダクトエンジニア(AWS環境)/KINTO CXシステム開発G/東京・名古屋
KINTO CXシステム開発グループについてTOYOTAのクルマのサブスクリプションサービスである『 KINTO 』を中心とした国内向けサービスのプロジェクト立ち上げから運用保守に至るまでの運営管理を行っています。大手EC、SIer、ベンチャー、Webサービス企業など、さまざまなスペシャリストが集まり、KINTOサービスを開発しています。
Follow Us
KINTOテクノロジーズの最新情報をSNSで発信中!イベント・テックブログ更新情報もお届けします。